
Securing Connected Robots: Cyber Threats in the Age of Generative AI
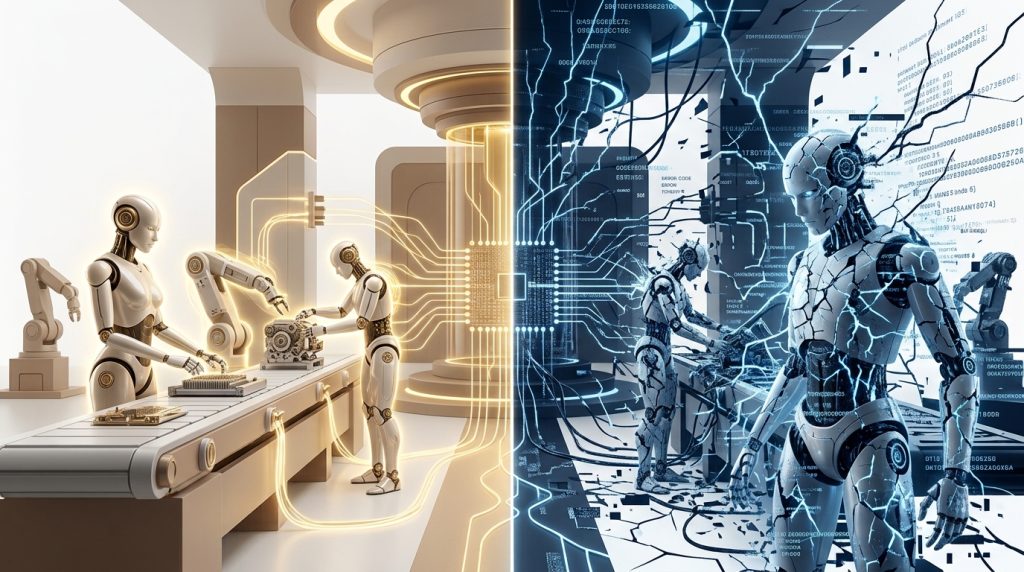
In an era where robots are being integrated into our daily lives at an accelerating pace—from smart robot vacuums to movement-enhancing exoskeletons—a pivotal question arises about the hackability of these systems. This article, based on the latest academic research and security reports, reveals a concerning reality: the use of generative AI in cyberattacks has demolished the technical barriers that once protected robots, turning them from helpful tools into easy targets for exploitation—and potentially into weapons. The article presents a systematic analysis of security vulnerabilities in robotic fleet management systems, drawing on real case studies of large-scale breaches, and discusses advanced protection mechanisms in the context of escalating threats.
First: The Shifting Threat Landscape in the Age of Generative AI
Traditional cybersecurity models in the robotics sector have long assumed that executing successful attacks requires deep technical expertise in embedded robotic systems and their communication protocols, such as ROS and ROS 2. But this assumption has become obsolete in the wake of the generative AI revolution. Recent research has proven that open-source AI tools, such as the Cybersecurity AI (CAI) framework, are capable of automating the discovery and exploitation of security vulnerabilities in consumer robots within hours—tasks that previously required security experts for months.
This shift reveals a dangerous asymmetry in the cyber power balance: while attackers have been armed with sophisticated AI tools, defensive measures still rely on traditional “defense in depth” concepts that are no longer adequate to counter the speed and intelligence of AI-powered attacks.
Second: Real Breach Cases: From Robot Vacuums to Exoskeletons
Accumulating evidence indicates that vulnerabilities in internet-connected robots are not theoretical but real and dangerous. Below are the most prominent documented cases:
1. Breach of a Fleet of Robot Vacuums (DJI Romo) – 2026
In an incident that exposed the fragility of cloud-based fleet management systems, a software engineer attempting to develop a remote-control app for his DJI Romo robot vacuum gained access to live cameras, microphones, home maps, and status data for approximately 7,000 robot vacuums across 24 countries. The root cause of the vulnerability was DJI’s cloud servers’ failure to validate the token for each device individually, granting the engineer owner-level privileges over this massive fleet of devices. The company later announced a fix, but the incident highlighted the grave risks arising from poor identity and privilege management in robotic fleet management platforms.
2. Critical Vulnerability in Yarbo Cloud Threatens a Global Robot Fleet
A security vulnerability (CVE-2026-7368) in the cloud infrastructure of Yarbo robots revealed a fundamental flaw in access control. The system was found not to enforce an authorization mechanism for each device or user, meaning any customer with valid credentials (whether shared or private) could subscribe to broad MQTT protocol topics covering all robots worldwide and publish control commands to any robot using the serial number exposed in the telemetry data stream. This vulnerability represents a blatant violation of the Principle of Least Privilege and creates a scenario in which compromising a single credential could lead to full control of the global robot fleet, potentially causing physical damage, data theft, or disruption of vital operations.
3. Hacking Three Robotic Systems Using Generative AI
In a pioneering academic study, researchers used the CAI framework to hack three different types of consumer robots, discovering 38 security vulnerabilities in record time:
-
Hookii Neomow lawn mower robot: An undocumented Android Debug Bridge (ADB) service was discovered on port 5555, granting researchers unrestricted root access to the robot’s system. From this position, they extracted hard-coded MQTT credentials used across the entire fleet, allowing them to connect to the EMQX server, enumerate 267 connected robots, and publish control commands to any of them. The analysis also revealed unencrypted data transmission (including GPS coordinates and 3D map data) and an internet-exposed MySQL database without protection.
-
Hypershell X exoskeleton: The BLE connection was found to require no authentication, allowing any device within range to connect and send control commands affecting user safety. A series of IDOR vulnerabilities were also identified, enabling retrieval of user and device information through unauthenticated APIs. Most critically, code analysis revealed plaintext SMTP and MySQL credentials, providing access to more than 3,300 internal emails containing sensitive information such as PayPal and Shopify account recovery codes.
-
HOBOT S7 Pro window-cleaning robot: 17 security vulnerabilities were identified, including unauthenticated BLE command injection and exploitation of over-the-air (OTA) firmware updates transmitted over plaintext HTTP.
4. Hacking Humanoid Robots via Voice Commands
At the GEEKCon competition in Shanghai, researchers from the DARKNAVY group demonstrated how weaknesses in AI systems embedded in Unitree humanoid robots could be exploited to control them via simple voice commands. More alarmingly, the team was able to use a compromised robot as a channel to propagate the attack to another robot that was not connected to the internet, via short-range wireless signals, demonstrating the ability of attacks to cascade across groups of machines. In a stark demonstration of physical consequences, an adversarial command was issued to the robot, causing it to advance toward a mannequin and strike it.
Third: Analysis of Attack Vectors in Connected Robots
The main attack vectors targeting robots and fleet management systems can be classified as follows, based on analytical studies and documented attacks:
1. Weaknesses in Architectural Layers
Connected robotic systems consist of several layers, each representing a potential attack surface:
-
Perception Layer: Includes cameras, LiDAR, radar, and GPS. It is exposed to spoofing, jamming, and data injection attacks, where an attacker can create phantom objects or hide real obstacles, misleading the decision-making system.
-
Communication Layer: Includes protocols such as MQTT, Wi-Fi, Bluetooth, and V2X. It is vulnerable to man-in-the-middle (MitM), denial-of-service (DoS), and eavesdropping attacks. Flat networks and lack of segmentation also allow lateral movement of attacks after initial compromise.
-
Application & Cloud Layer: Includes APIs, cloud management platforms, and OTA updates. Cases such as the DJI Romo and Yarbo breaches showed that weaknesses in authentication and authorization at this level can lead to control of an entire fleet of devices.
2. Cases Targeting Traditional Fleet Management Systems
Risks are not limited to consumer robots but extend to commercial vehicle fleet management systems. In October 2024, a UK vehicle tracking service provider suffered a cyberattack that disrupted tracking systems, alarms in prison vehicles, and courier trucks. In another incident, vulnerabilities in the SinoTrack GPS platform revealed the ability to track and remotely control vehicles, including the ability to cut off the fuel supply. These incidents confirm that attacks on critical logistics infrastructure can cause widespread economic damage.
Fourth: Protection and Defense Mechanisms: Toward an Integrated Security Layer for Robots
Facing this evolving threat landscape, securing robots and fleet systems requires moving beyond traditional security solutions and adopting an integrated, multi-layered defense framework:
1. AI-Native Defense
As attacks become automated and AI-driven, defenses must evolve at the same pace. Researchers suggest the need to develop “GenAI-Native” defensive agents capable of matching the speed and adaptability of automated attacks. This includes:
-
ML-based intrusion detection systems (IDS) to detect anomalous patterns in network traffic and vehicle behavior in real time.
-
Physics-aware anomaly detection that monitors the robot’s actual behavior to detect inconsistencies that may indicate an attack on the control loop, such as sensor drift or injected control signals.
2. Identity and Access Management (IAM)
A unified identity layer must be established covering the robot, the operator, operations, and contracts. This requires:
-
Secure by Default in middleware systems such as ROS2, which offer encryption and authentication mechanisms but are disabled by default and difficult to configure.
-
Adopting a Zero Trust Architecture that assumes no trusted internal party and applies the principle of least privilege and continuous verification.
-
Addressing cloud-level security vulnerabilities by enforcing authorization mechanisms for each device and user, as demonstrated in the Yarbo vulnerability.
3. Supply Chain & OTA Security
Attacks targeting firmware updates (OTA) pose a major risk, as compromising a single update package can propagate across an entire fleet. Solutions include:
-
Strong authentication of updates using digital signatures and rollback protection mechanisms.
-
Standardizing Software Bills of Materials (SBOM) using standards such as SPDX and CycloneDX for supply chain transparency, as required by legislation such as the European Cyber Resilience Act.
4. Physical & Control Layer Security
Since robots are cyber-physical systems, their security requires protecting the control loop:
-
Using Trusted Platform Modules (TPM) and Hardware Security Modules (HSM) to secure physical and digital layers and store encryption keys securely.
-
Implementing control-aware intrusion detection mechanisms to detect any attempts to manipulate control or timing signals.
-
Adopting a proactive approach through threat modeling and regular penetration testing to identify vulnerabilities before they are exploited, as demonstrated in Attack-Defense Trees (ADT) methodologies.
Fifth: Conclusion and Future Outlook
The security assessment of internet-connected robotic systems indicates a critical gap between the speed at which threats are evolving—enhanced by generative AI technologies—and the slow development of traditional defenses. Studies and documented incidents have proven that security vulnerabilities are not merely theoretical weaknesses but real gateways that can lead to large-scale control of robot fleets, with consequences ranging from privacy violations to severe physical damage.
The path toward a secure future for robots requires a qualitative shift in cybersecurity culture, starting from the design phase and integrating AI-powered defenses, rigorous identity and access security engineering, supply chain security, and physical layer protection. As industry experts note, the robotics sector today resembles the cloud computing sector in the early 2010s: tremendous growth accompanied by significant security risks—but with awareness of these risks and the development of appropriate solutions, a resilient and secure robotic infrastructure can be built for the future.
Sources and References
-
MITRE. (2026). CVE-2026-7368 – Yarbo Cloud Authorization Flaw. VulDB.
-
Popular Science. (2026). Man accidentally gains control of 7,000 robot vacuums.
-
Mayoral-Vilches, V., et al. (2026). Cybersecurity AI: Hacking Consumer Robots in the AI Era. arXiv preprint arXiv:2603.08665.
-
Interesting Engineering. (2025). China: Single voice command exposes humanoid robots to hijacking and cascading attacks.
-
Upstream Security. (2025). 2025 Global Automotive Cybersecurity Report.
-
Help Net Security. (2025). SinoTrack GPS vulnerabilities may allow attackers to track, control vehicles.
-
TechTarget. (2025). Fleet telematics company discovers unauthorized data transmissions.
-
Sekyere, Y. O. M., et al. (2026). Security Challenges and Solutions in Self-Driving Vehicles: A Comprehensive Review. IET Intelligent Transport Systems.
-
Venkat, V. (2026). The Missing Layers in the Robotics Security Stack. RoboticsTomorrow.
-
Scientific Reports. (2026). Robotic systems in internet of things: addressing security challenges through threat modeling and penetration testing. Nature, 16, 18325.
-
ScienceDirect. (2025). Cyber-resilient autonomous vehicles: securing networks and enhancing decision-making with next-gen security measures.
-
IEEE Xplore. (2025). Securing Digital Twins in Autonomous Vehicles: Cyber Threats, Mitigation Strategies, and Innovative Security Solutions.
-
IEEE Xplore. (2025). Automotive Hacking: Security Risks in Connected and Autonomous Vehicles.